Bold Reports® v5.x or Older Installation and Deployment on Ubuntu
You can install Bold Reports® version 5.x or older on Ubuntu by installing the required packages and running the Bold Reports® Linux package installer. You can also configure Nginx as a reverse proxy manually and secure the site with SSL.
What do I need before installing Bold Reports® on Ubuntu?
Bold Reports® on Ubuntu needs a sudo-enabled user account, Nginx, zip, GDIPlus and an OpenSSL configuration path.
-
Access to a Linux server with a standard user account and sudo privileges.
-
Install
Nginxby running the following commands:sudo apt-get updatesudo apt-get install nginx -
Install
zipby running the following command:sudo apt-get install zip -
Install the
GDIPluspackage by running the following command:sudo apt-get install libgdiplus -
Add an
openssl confpath in the environment if it does not exist.export OPENSSL_CONF=/etc/ssl/
How do I configure the Bold Reports® application on Ubuntu?
You configure Bold Reports® on Ubuntu by downloading the Linux package, extracting it, and running the install-boldreports.sh script.
-
Register and download the Bold Reports® Linux package from the registration and download section.
-
Download the Bold Reports® Linux package by running the following command:
sudo wget {Bold Reports Linux package link} -
Extract the zip file by running the following command:
sudo unzip {Bold Reports Linux package zip file} -
Change the directory to
BoldReports_EnterpriseReporting-Linuxby running the following command:cd BoldReports_EnterpriseReporting-Linux -
Run the following command to deploy Bold Reports® on your Linux machine:
sudo bash install-boldreports.sh -i {new} -u {user} -h {host URL} -n {true or false}-
i: Installation type. Specifies whether it is a new or upgrade installation.
-
u: The user or group that manages the service.
-
h: Domain or IP address of the machine with HTTP protocol.
-
n: Set this to
trueto configure Bold Reports® with the Nginx front-end server automatically.
IMPORTANT: If existing applications on that Linux machine use Nginx, set the “-n” value to false and configure Nginx manually.
Example for a new installation:
sudo bash install-boldreports.sh -i new -u www-data -h http://linux.example.com -n true -
After the Bold Reports® installation is complete, open the host URL in the browser and continue the application startup.
What changes after upgrading from v3.1.x to v5.2.26?
Bold Reports® v5.2.26 needs updated reportservice and viewer sections in the Nginx configuration file when you upgrade from v3.1.x with manual Nginx configuration.
Note:
- After upgrading the Bold Reports® application to v5.2.26 from v3.1.x, update the following section of the reportservice and viewer codes in the Nginx configuration file in the location
/etc/nginx/sites-available.- Make this breaking change only for manual Nginx configuration.
Update the reportservice and viewer codes in the Nginx configuration file as follows:
    location /reporting/reportservice {
        root               /var/www/bold-services/application/reporting/reportservice;
        proxy_pass         http://localhost:6553;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /reporting/viewer {
        proxy_pass         http://localhost:6554/reporting/viewer;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
The following screenshot shows the updated Nginx configuration.
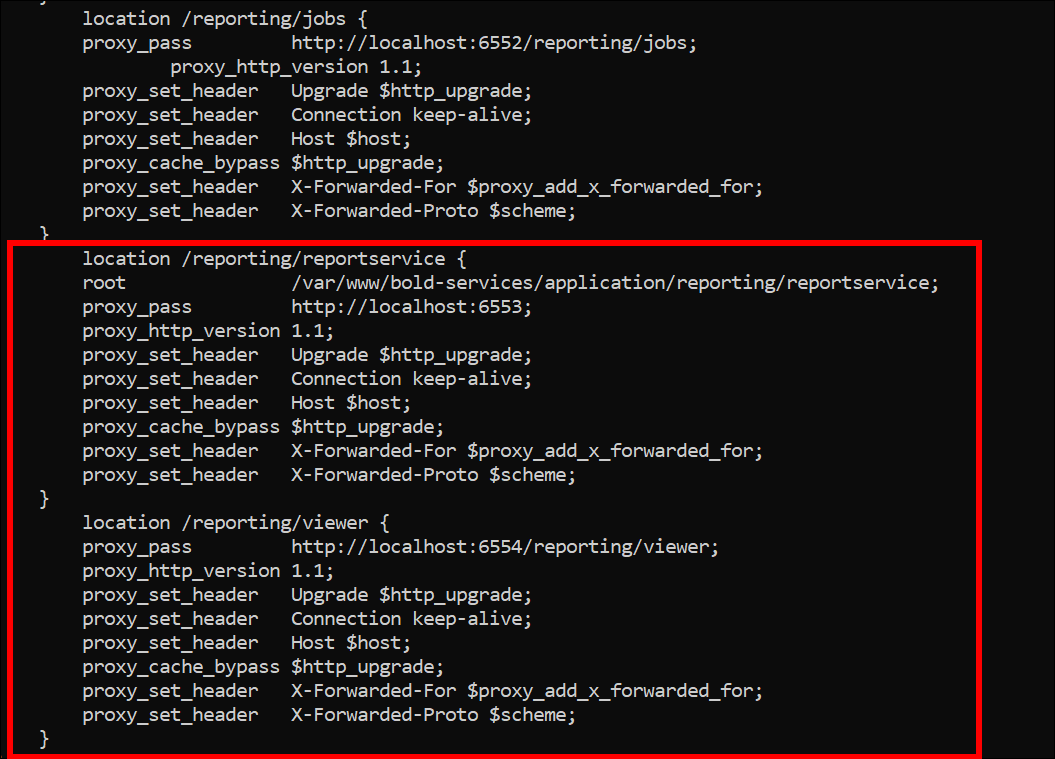
After you update the Nginx configuration, run sudo nginx -t to verify the syntax of the configuration files. If the configuration file test is successful, run sudo nginx -s reload to force Nginx to pick up the changes.
Manually configure Nginx
You configure Nginx manually as a reverse proxy that forwards requests to the Bold Reports® app. Modify /etc/nginx/sites-available/default: open it in a text editor and add the following code:
       #server {
       #listen 80;
       #server_name example.com;
       #return 301 https://example.com$request_uri;
       #}

         server {
       listen        80 default_server;

       #server_name   example.com;

       #listen 443 ssl;
       #ssl on;
       #ssl_certificate /path/to/certificate/file/domain.crt;
       #ssl_certificate_key /path/to/key/file/domain.key;

       proxy_read_timeout 300;
       proxy_connect_timeout 300;
       proxy_send_timeout 300;
       send_timeout 300;
       client_max_body_size 200M;

       location / {
      root /var/www/bold-services/application/idp/web/wwwroot;
        proxy_pass http://localhost:6500/;
        proxy_http_version 1.1;
        proxy_set_header Upgrade $http_upgrade;
        proxy_set_header Connection keep-alive;
        proxy_set_header Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header X-Forwarded-Proto $scheme;
        fastcgi_buffers 16 16k;
        fastcgi_buffer_size 32k;
    }
    location /api {
        proxy_pass         http://localhost:6501/api;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /ums {
        root               /var/www/bold-services/application/idp/ums/wwwroot;
        proxy_pass         http://localhost:6502/ums;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /ums/signalr/progresshub {
        proxy_pass         http://localhost:6502/ums/signalr/progresshub;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection "upgrade";
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /reporting {
    root /var/www/bold-services/application/reporting/web/wwwroot;
        proxy_pass         http://localhost:6550/reporting;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /reporting/messageHub {
        proxy_pass         http://localhost:6550/reporting/messageHub;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection "upgrade";
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /reporting/api {
        proxy_pass         http://localhost:6551/reporting/api;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /reporting/jobs {
        proxy_pass         http://localhost:6552/reporting/jobs;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /reporting/reportservice {
        root               /var/www/bold-services/application/reporting/reportservice;
        proxy_pass         http://localhost:6553;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
    location /reporting/viewer {
        proxy_pass         http://localhost:6554/reporting/viewer;
        proxy_http_version 1.1;
        proxy_set_header   Upgrade $http_upgrade;
        proxy_set_header   Connection keep-alive;
        proxy_set_header   Host $host;
        proxy_cache_bypass $http_upgrade;
        proxy_set_header   X-Forwarded-For $proxy_add_x_forwarded_for;
        proxy_set_header   X-Forwarded-Proto $scheme;
    }
}
After you set up the Nginx configuration, run sudo nginx -t to verify the syntax of the configuration files. If the configuration file test is successful, run sudo nginx -s reload to force Nginx to pick up the changes.
How do I configure SSL?
You can configure the Bold Reports® site with your SSL certificate if you have one for your domain. Follow these steps, or skip them if you do not need SSL:
-
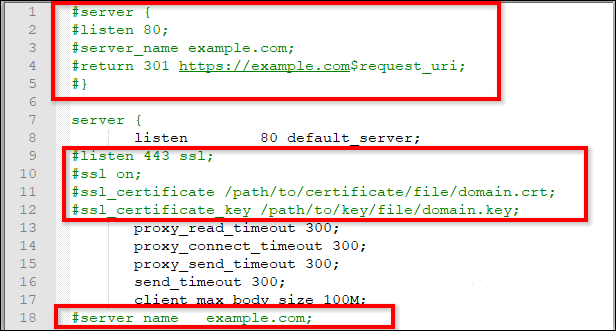
Uncomment the following marked lines in the Nginx config file. The screenshot shows the SSL lines to uncomment.
-
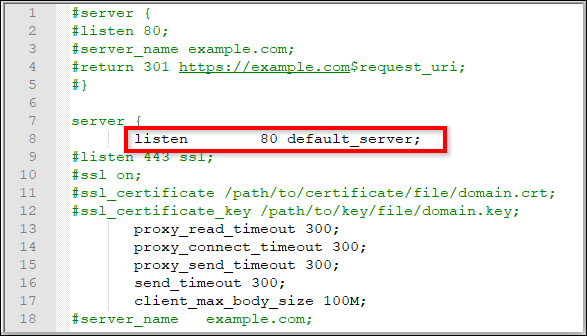
Comment out the following marked line in the Nginx config file. The screenshot shows the line to comment out.
-
Replace
example.comwith your domain name. -
Define the path of the SSL certificate:
ssl_certificate /etc/ssl/domain.crt. -
Specify the directory where the SSL certificate key is located:
ssl_certificate_key /etc/ssl/domain.key. -
Save the file and run sudo
nginx -tto verify the syntax of the configuration file. If the configuration file test is successful, runsudo nginx -s reloadto force Nginx to pick up the changes.
NOTE: If you configure the application with SSL, update the URLs in the product. json with
HTTPS. The file is located in/var/www/bold-services/application/app_data/configuration.
Frequently asked questions
Which file do I edit to configure Nginx manually on Ubuntu?
For Bold Reports® on Ubuntu, modify /etc/nginx/sites-available/default and add the reverse proxy code.
What must I update after enabling SSL?
After you configure Bold Reports® with SSL, update the URLs in the product.json with HTTPS in /var/www/bold-services/application/app_data/configuration.