Set up JWT single sign-on in Bold Reports® User Management Server
To set up JWT single sign-on (SSO) in Bold Reports®, enable and configure the custom JSON Web Token (JWT) settings on the User Management Server administration page.
How do I configure JWT in Bold Reports®?
To configure JWT in the Bold Reports® User Management Server, follow these steps:
-
Log in with the URL
{Bold Reports URL}/ums/administrationusing the admin credentials. -
Click
Authenticationand thenJWT.
-
Enable the JWT settings.
-
Provide the following details in the
JWTsettings.Name It represents the name of the JWT provider to be displayed on the login page. Provider Logo It represents the logo of the JWT provider to be displayed on the login page. Remote Login URL This is the endpoint of the JWT provider used to send the authorization request from the Bold Reports® application. Remote Logout URL It is the endpoint of the JWT provider to send the logout request once the user logged out in the Bold Reports® application. -
After you save the values, the application generates a
Signing Key. Use this signing key to sign JSON Web Tokens from your application. -
Copy, view, or reset the
Signing Keywith the following options: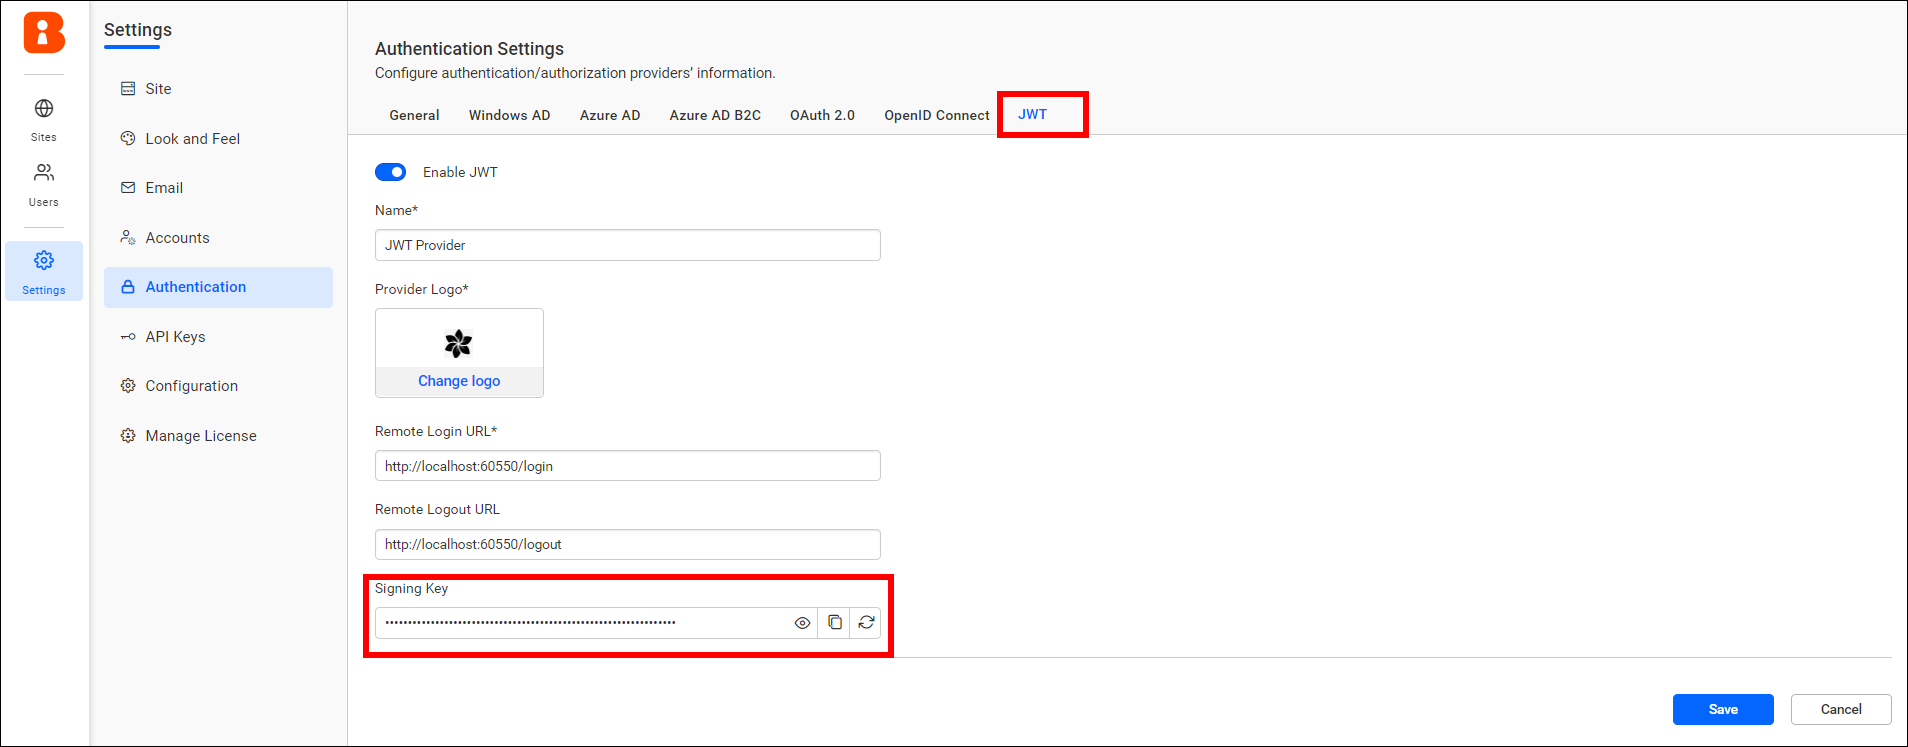
How does JWT work with Bold Reports®?
JWT single sign-on in Bold Reports® works in the following sequence:
-
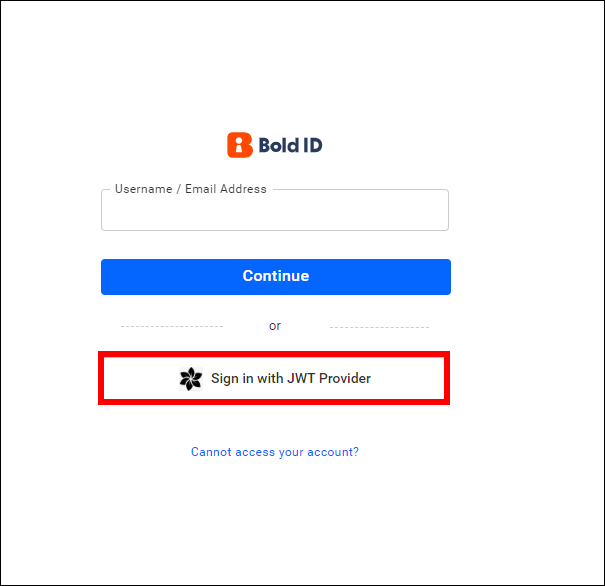
After the JWT settings are configured, go to the Bold Reports® login page and click the JWT login option. You are redirected to the configured application login URL.
-
The application generates the JSON Web Token for the user and redirects back to Bold Reports® call back URL
{Bold Reports URL}/sso/jwt/callback?jwt={token}&site_identifier={site identifier}&redirect_to={redirecturl}with the encoded JWT in a query string. -
The Bold Reports® application validates the JWT and deserializes the user information from the token.
-
From the user information, the Bold Reports® application checks whether the user’s email already has access to the Bold Reports® application. If the user is already available in Bold Reports®, the application authenticates the user.
-
If the user is not available in the Bold Reports® server, the application adds the user and authenticates the user to access the Bold Reports® application.
JWT Callback URL
The Bold Reports® JWT callback URL validates the JWT response from the configured application.
After a successful login to your configured application, users can be redirected to the specified URL.
{Bold Reports URL}/sso/jwt/callback?jwt={token}&site_identifier={site identifier}&redirect_to={redirecturl}
| Parameter | Required | Comments |
|---|---|---|
| jwt | Yes | The JSON Web Token will be passed in this parameter, containing the JWT Payload |
| site_identifier | No | This parameter will be used to grant site access for the JWT user.
If the JWT login accessed from the tenant, the Bold Reports® login URL will redirect to your application with the tenant site identifier in the URL query string. You can use this identifier in the JWT response URL. Example Url
|
| redirect_to | No | If this parameter is included in the JWT response, the user will be redirected to the corresponding page after the login process is completed. |
How do I create the JSON Web Token?
To create a JWT for Bold Reports®, use HMAC-SHA256 as the signing algorithm.
What parameters can be passed in the payload of JWT
A JWT for Bold Reports® should include the following claims:
| Parameter | Parameter Name | Value Type | Required | Comments |
|---|---|---|---|---|
| User Id | sub | string | Yes | Unique identifier of the user. |
| string | Yes | Email address of the user. | ||
| First Name | first_name | string | Yes | First name of the user. |
| Last Name | last_name | string | No | Surname of the user. |
| Phone | phone | string | No | Phone number of the user. |
JSON Web Token sample
The following C# sample shows how to generate a JWT for Bold Reports®:
private string GenerateJSONWebToken(UserModel userInfo)
{
    var signingKey = "signingkey";// Signing key value will copy from JWT Settings page
    var securityKey = new SymmetricSecurityKey(Encoding.UTF8.GetBytes(signingKey));
    var credentials = new SigningCredentials(securityKey, SecurityAlgorithms.HmacSha256Signature, SecurityAlgorithms.Sha256Digest);

    var claims = new[] {
        new Claim("sub", "420c5d51-1754-4a9b-b4b5-d5bfebb21b0f")
        new Claim("email", "[email protected]"),
        new Claim("first_name", "Makila"),
        new Claim("last_name", "S"),
        new Claim("phone", "1234567890")
            };

    var token = new JwtSecurityToken(claims: claims,
                expires: DateTime.Now.AddMinutes(120),
                signingCredentials: credentials);

    return new JwtSecurityTokenHandler().WriteToken(token);
}
Frequently asked questions
Which signing algorithm does Bold Reports® JWT use?
Use HMAC-SHA256 as the signing algorithm, with the Signing Key generated on the JWT settings page.
What happens if a JWT user does not exist in Bold Reports®?
The application adds the user and authenticates the user to access the Bold Reports® application.
Can I pass more than one site identifier?
No. Only one site identifier should be passed in the callback URL.