Connect to AWS Secrets Manager
Bold Reports® connects to AWS Secrets Manager to retrieve database credentials dynamically, so you can connect to your chosen database (e.g. SQL Server, PostgreSQL, and MySQL) within reports. This enhances security by centralizing credential management.
How do I create a secret in AWS Secrets Manager?
Before you connect Bold Reports® to AWS Secrets Manager, create and configure a secret in your AWS account. The secret stores the credentials for your database.
-
Sign in to the AWS Management Console and open the Secrets Manager console at the AWS Secrets Manager Console.
-
In the Secrets Manager console, choose the
Secretsoption from the left navigation panel, then clickStore a new secret.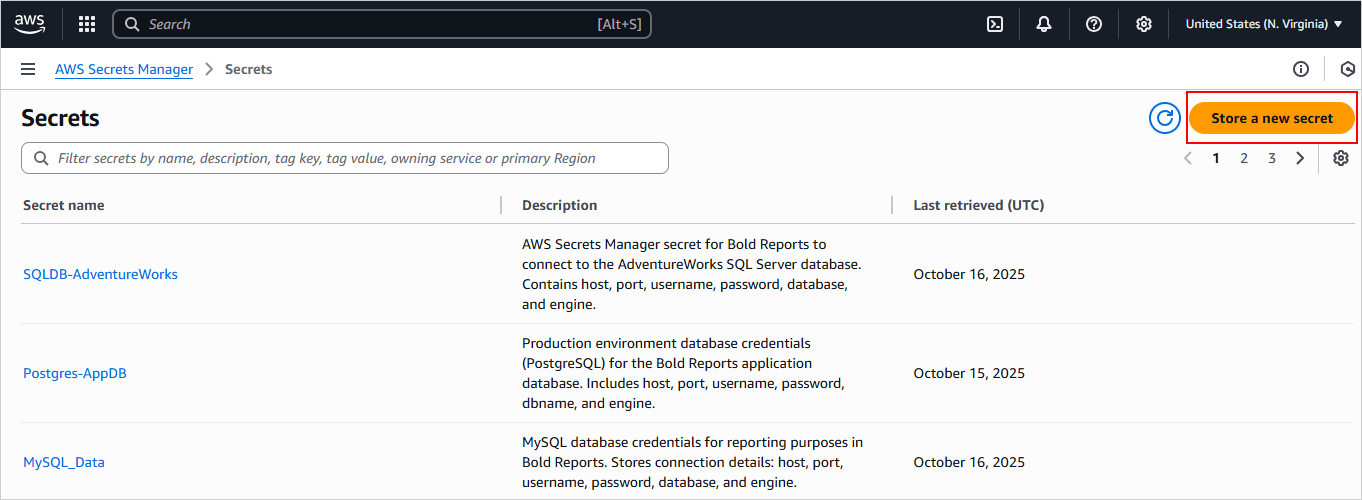
-
On the Choose secret type page, select the
Other type of secretoption. With this option, you can manually define the key-value pairs or provide a custom JSON string for your database credentials.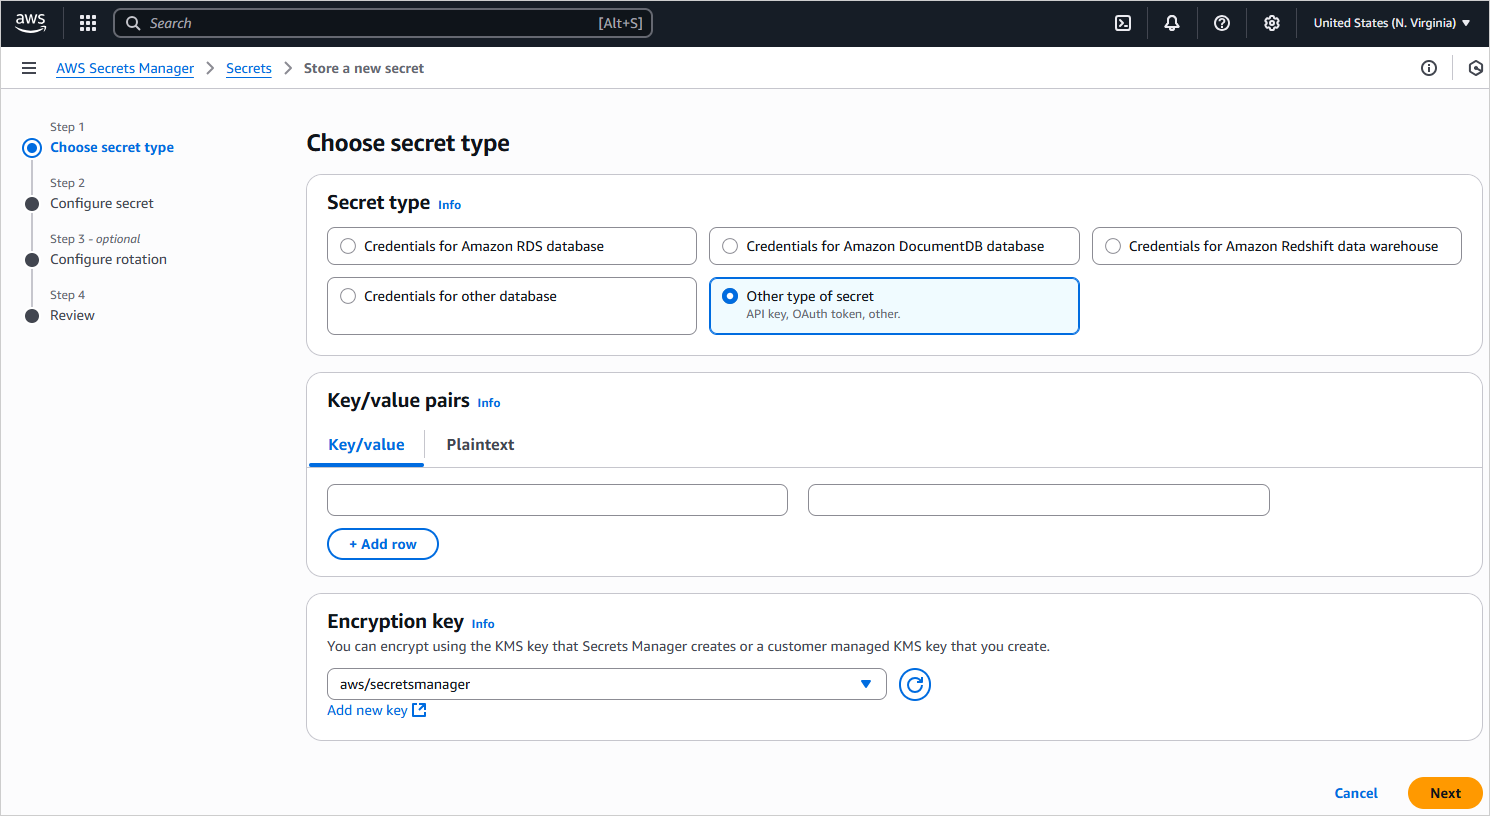
-
In the Key/value pairs section, select the Key/value option, then add your database credentials as individual key-value pairs. For proper integration with Bold Reports®, use the following valid keys:
Engine Valid Keys SQL Server server, data source, initial catalog, database, user id, uid, pwd, password, trusted_connection, integrated security, persist security info, encrypt, trustservercertificate, certificate, port, connect timeout, connection timeout MySQL server, host, port, database, db, uid, user id, userid, username, user, user name, pwd, password, sslmode, ssl mode, tlsversion, ssl-ca, sslcert, sslkey, sslverify, use compression, persist security info, allow public key retrieval, connection timeout, connect timeout, default command timeout PostgreSQL server, host, port, database, db, username, user id, uid, user name, pwd, password, sslmode, ssl mode, sslrootcert, sslcert, sslkey, sslcrl, trust server certificate, connect timeout, command timeout, timeout, client_encoding, options, keepalives, keepalives_idle, keepalives_interval, keepalives_count, integrated security, persist security info 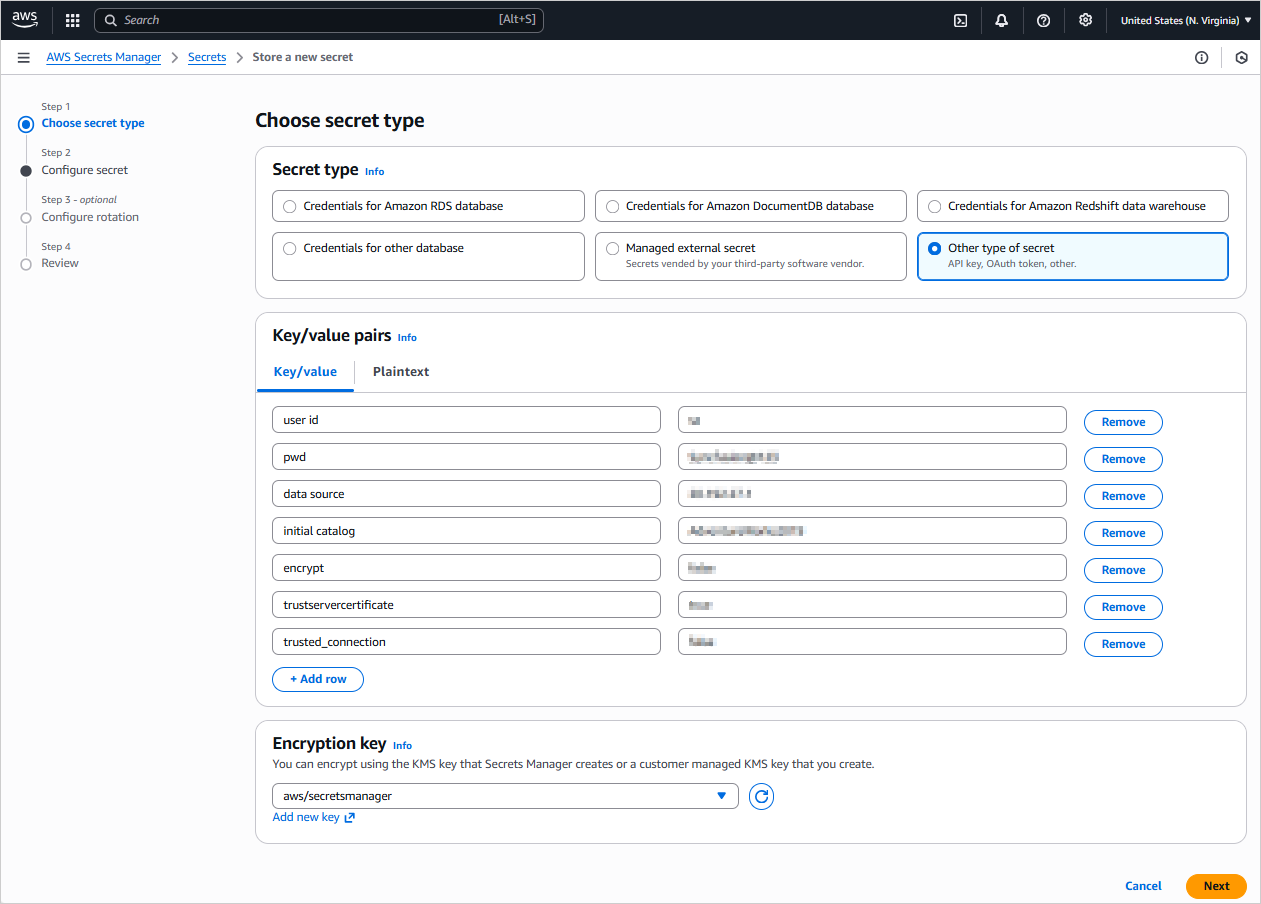
-
In the Configure secret section, enter a
Secret name. You use thisSecret Namelater when you configure the data source in Bold Reports®. Optionally, add aDescription. ClickNext, then complete the remaining configuration steps (for example rotation settings) until you reach the finalReviewpage.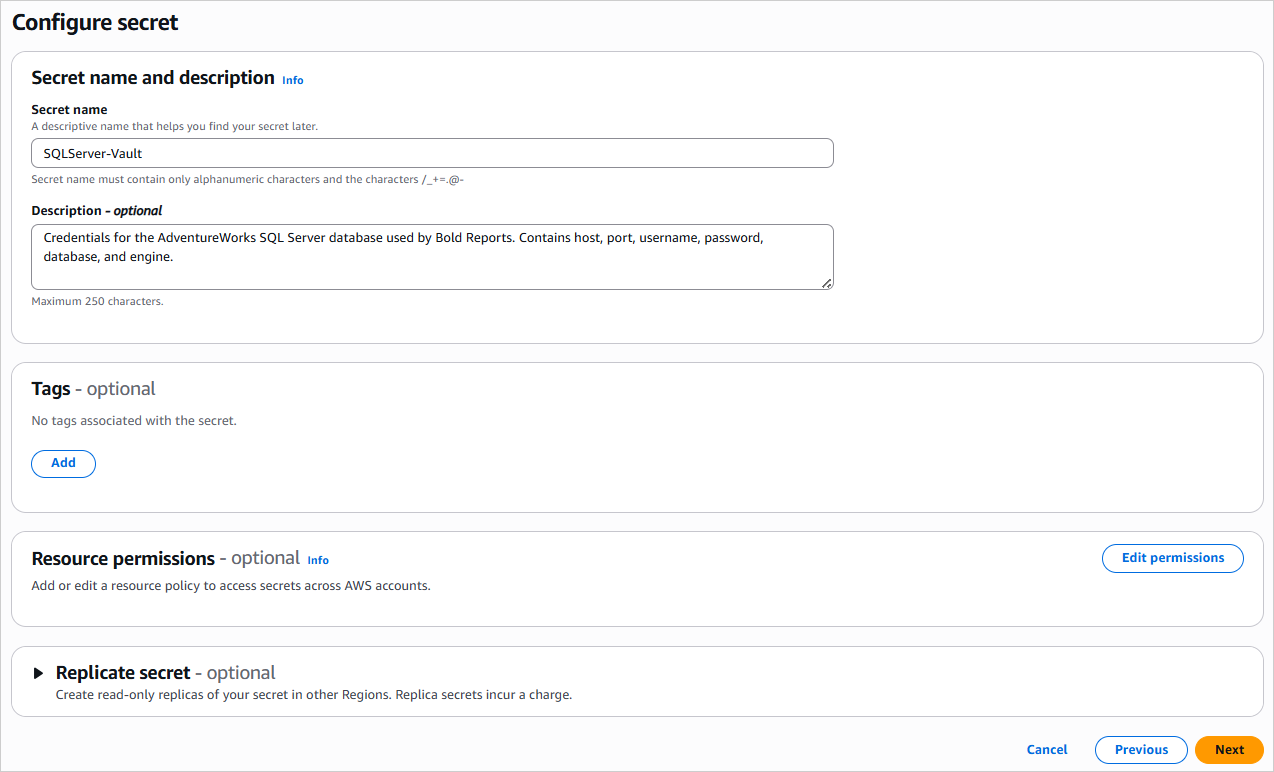
-
In the
Reviewsection, verify all your settings, then click theStoreoption to finalize the creation of your secret.
Your secret is now created and ready to be accessed by Bold Reports®.
How do I create an AWS Secrets Manager data source?
To create an AWS Secrets Manager data source in the Bold Reports® Web Report Designer, open the Data configuration panel and enter your AWS details.
- Click the Data icon in the configuration panel.
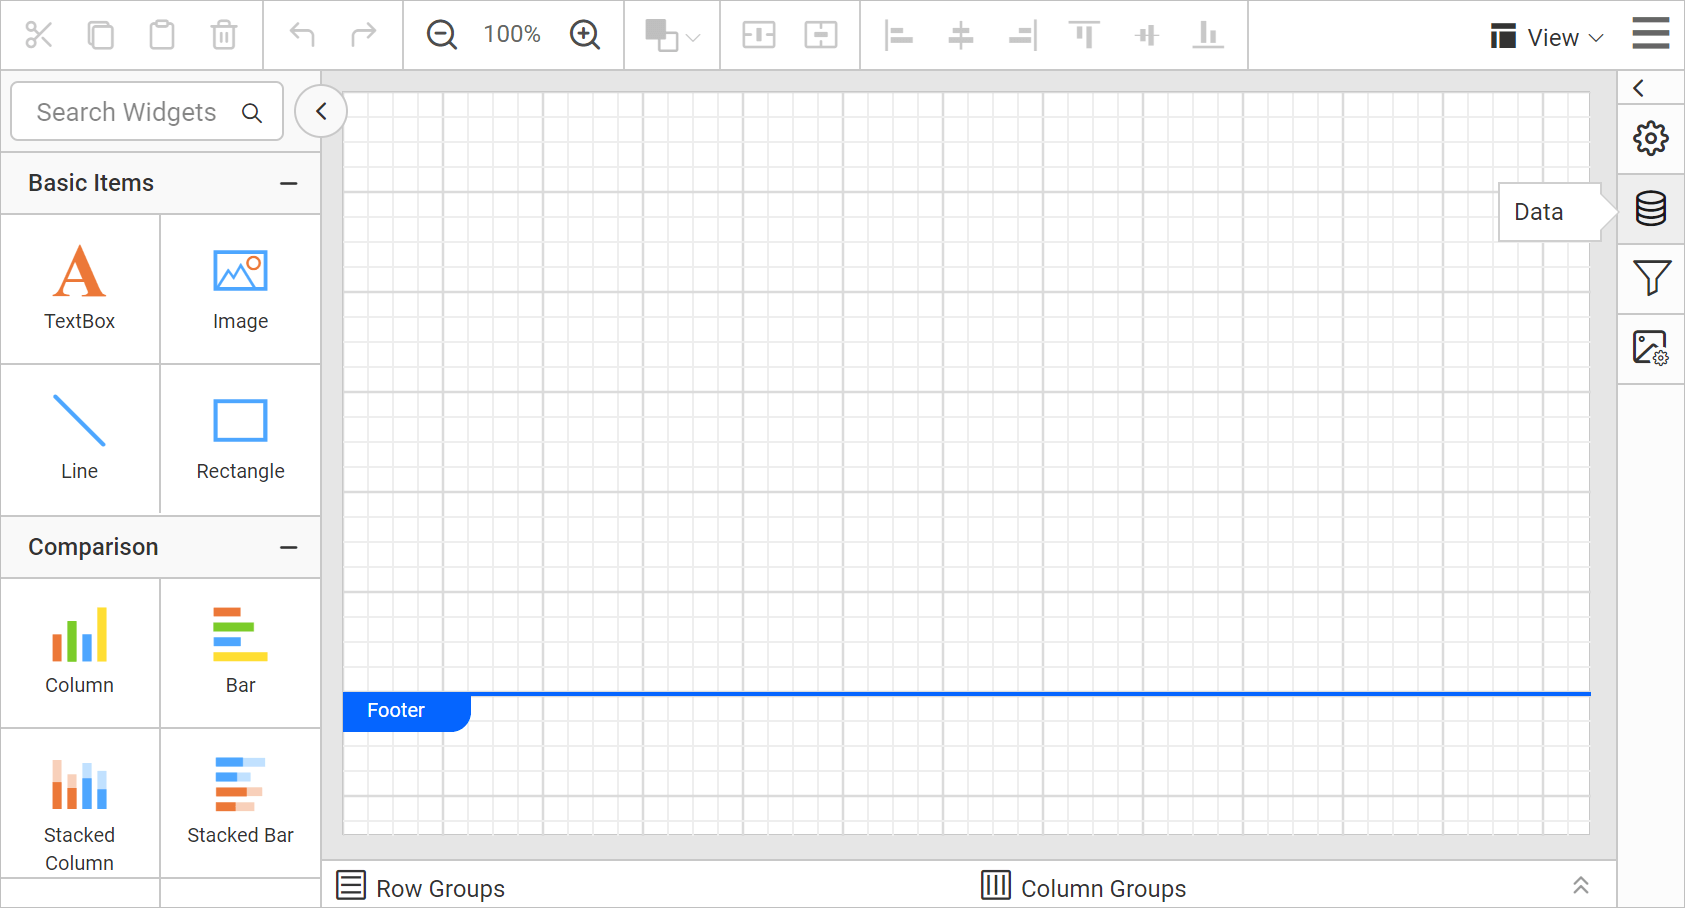
- In the
DATAconfiguration panel, click theNEW DATAoption.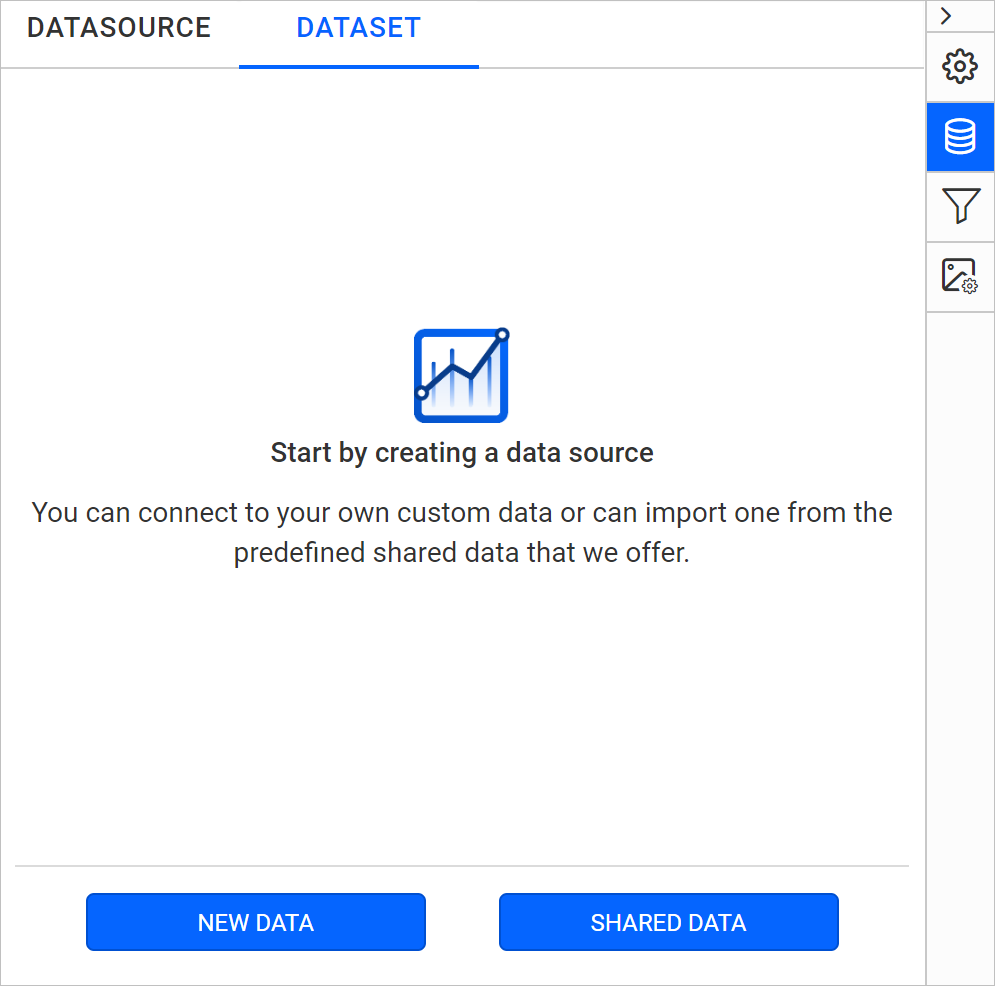
- In the Connection type panel, select
AWS Secrets Manageras the data source type.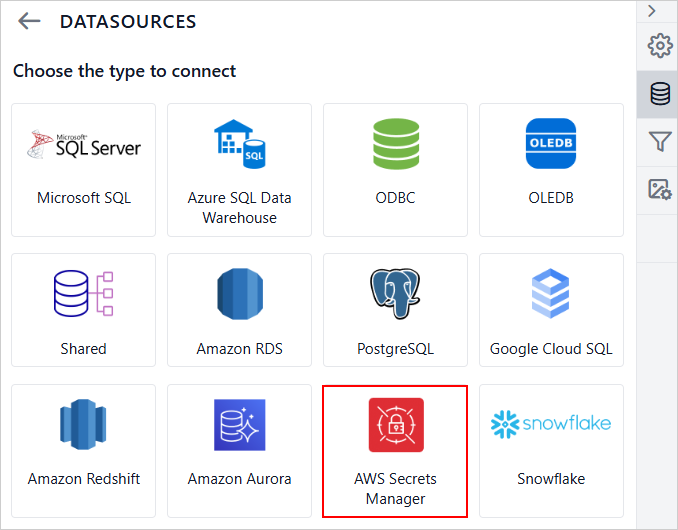
- In the
NEW DATASOURCEpanel, provide the following details:- Specify the data source name without special characters in the Name field.
- Select
SQL Serverfrom the Database Engine drop-down to use with the configured AWS Secrets Manager secret. - Enter your AWS Access Key ID in the Access Key text box. The Access Key ID authenticates requests to AWS.
- Enter your AWS Secret Access Key in the Secret Access Key text box. The Secret Access Key works with the Access Key ID for authentication.
- Enter the Region where your AWS Secrets Manager secret is stored (e.g., us-east-1).
- From the Secret Name drop-down, select the secret that contains your database credentials in AWS Secrets Manager (e.g., SQLServer-Vault). The selected secret is expected to contain the following SQL Server connection string key-value pairs: data source, user id, pwd, initial catalog, encrypt, trustservercertificate and trusted_connection.
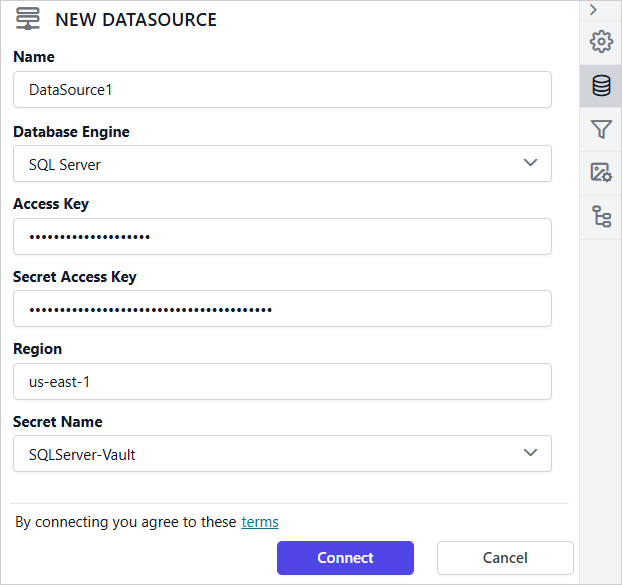
- Click the
Connectoption to connect Bold Reports® with the Microsoft SQL Server database. - Drag and drop the table from the table schema in the query design view page.
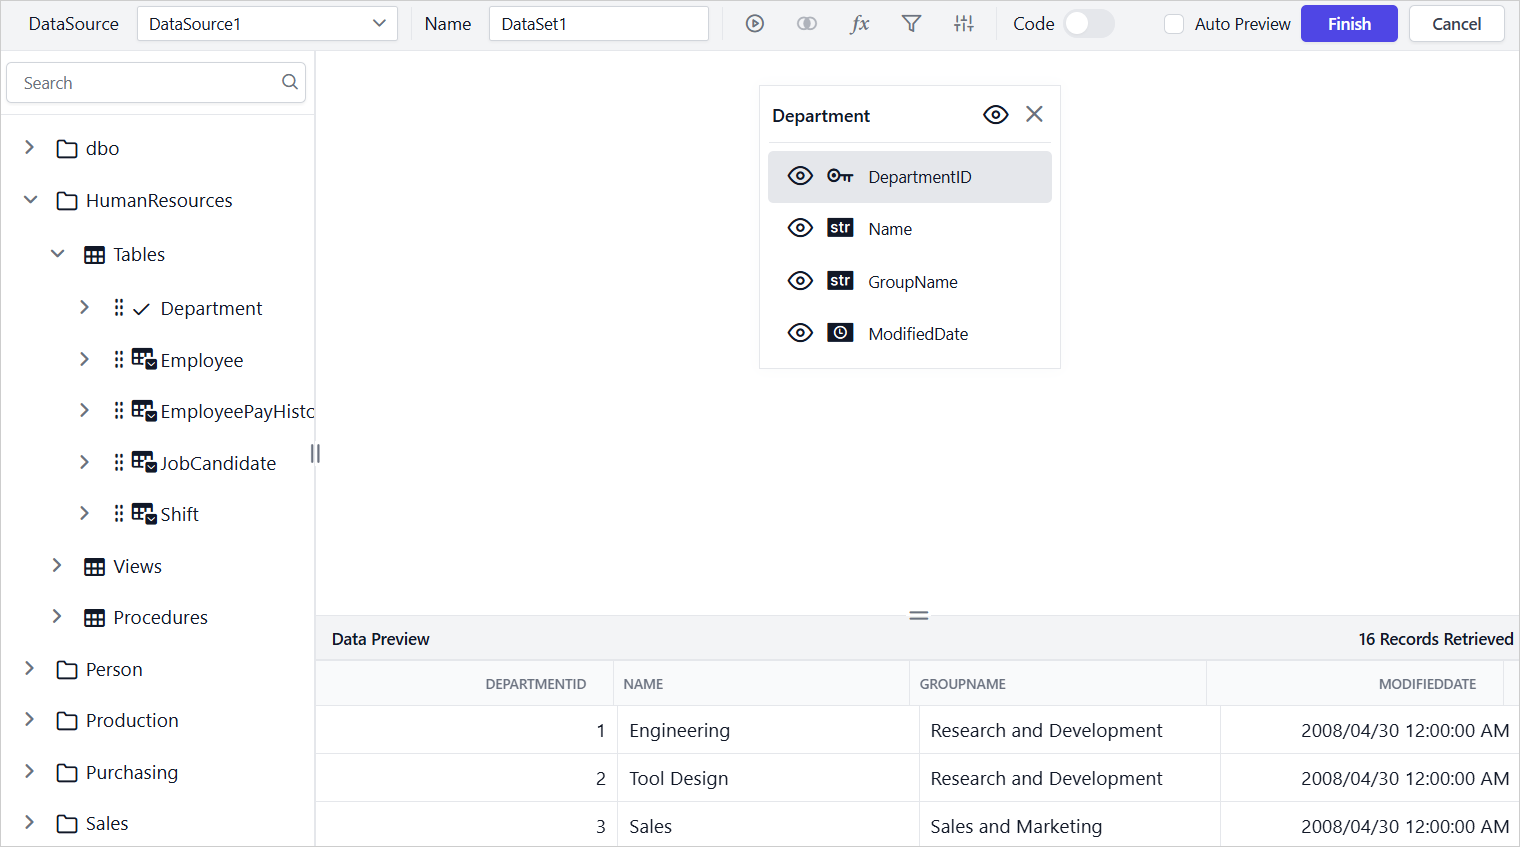
- Click the
Finishoption to save the data source with a relevant name and continue designing the report.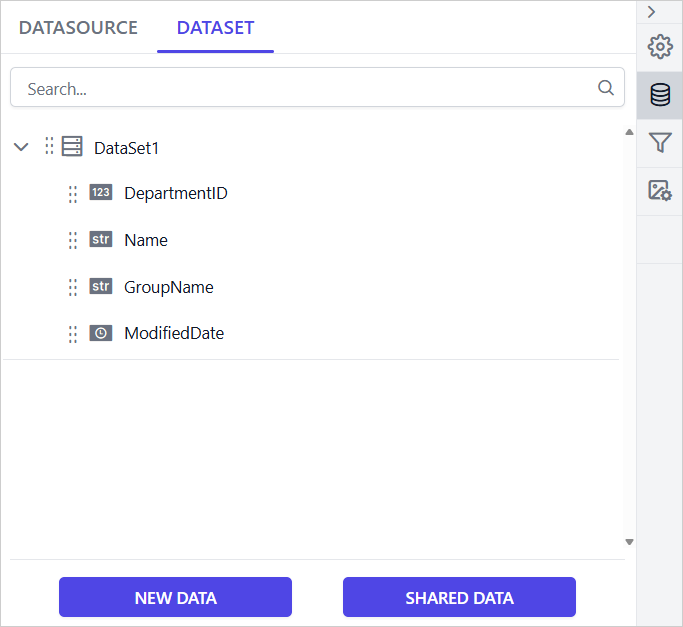
AWS Secrets Manager supported database engine in Bold Reports®
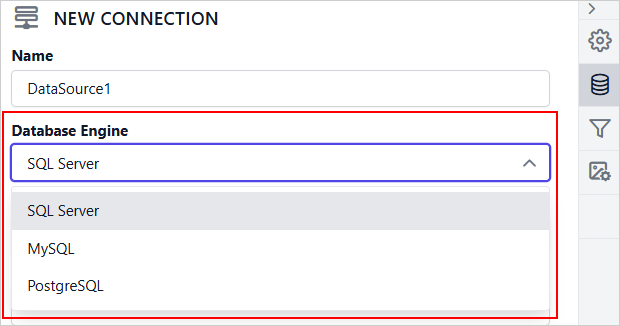
Bold Reports® supports the following database engines with AWS Secrets Manager:
- SQL Server
- MySQL
- PostgreSQL
The following image shows the Database Engine drop-down.
Frequently asked questions
Why use AWS Secrets Manager with Bold Reports®?
Bold Reports® retrieves database credentials from AWS Secrets Manager dynamically. This enhances security by centralizing credential management.
Which secret type should I choose in AWS Secrets Manager?
Select the Other type of secret option. You can then define key-value pairs or provide a custom JSON string for your database credentials.
What AWS details do I need for the data source?
You need your AWS Access Key ID, Secret Access Key, the Region where the secret is stored, and the Secret Name.