Keycloak support for SSO authentication in Bold Reports®
You can let Keycloak users sign in to Bold Reports® with single sign-on by registering Bold Reports® as an OpenID Connect client in Keycloak.
The following steps show how to register Bold Reports® in Keycloak and connect it through OpenID Connect.
How to register the Bold Reports® application in Keycloak
You register the Bold Reports® application as an openid-connect client in Keycloak.
NOTE: This configuration has to be done on the Keycloak website.
What do I need before I register Bold Reports® in Keycloak?
To register Bold Reports® in Keycloak, you need the following:
- An admin account in Keycloak.
- Install the Bold Reports® application.
How do I register the Bold Reports® application in Keycloak?
You create a Keycloak client for Bold Reports® from the Security admin console. Follow these steps:
-
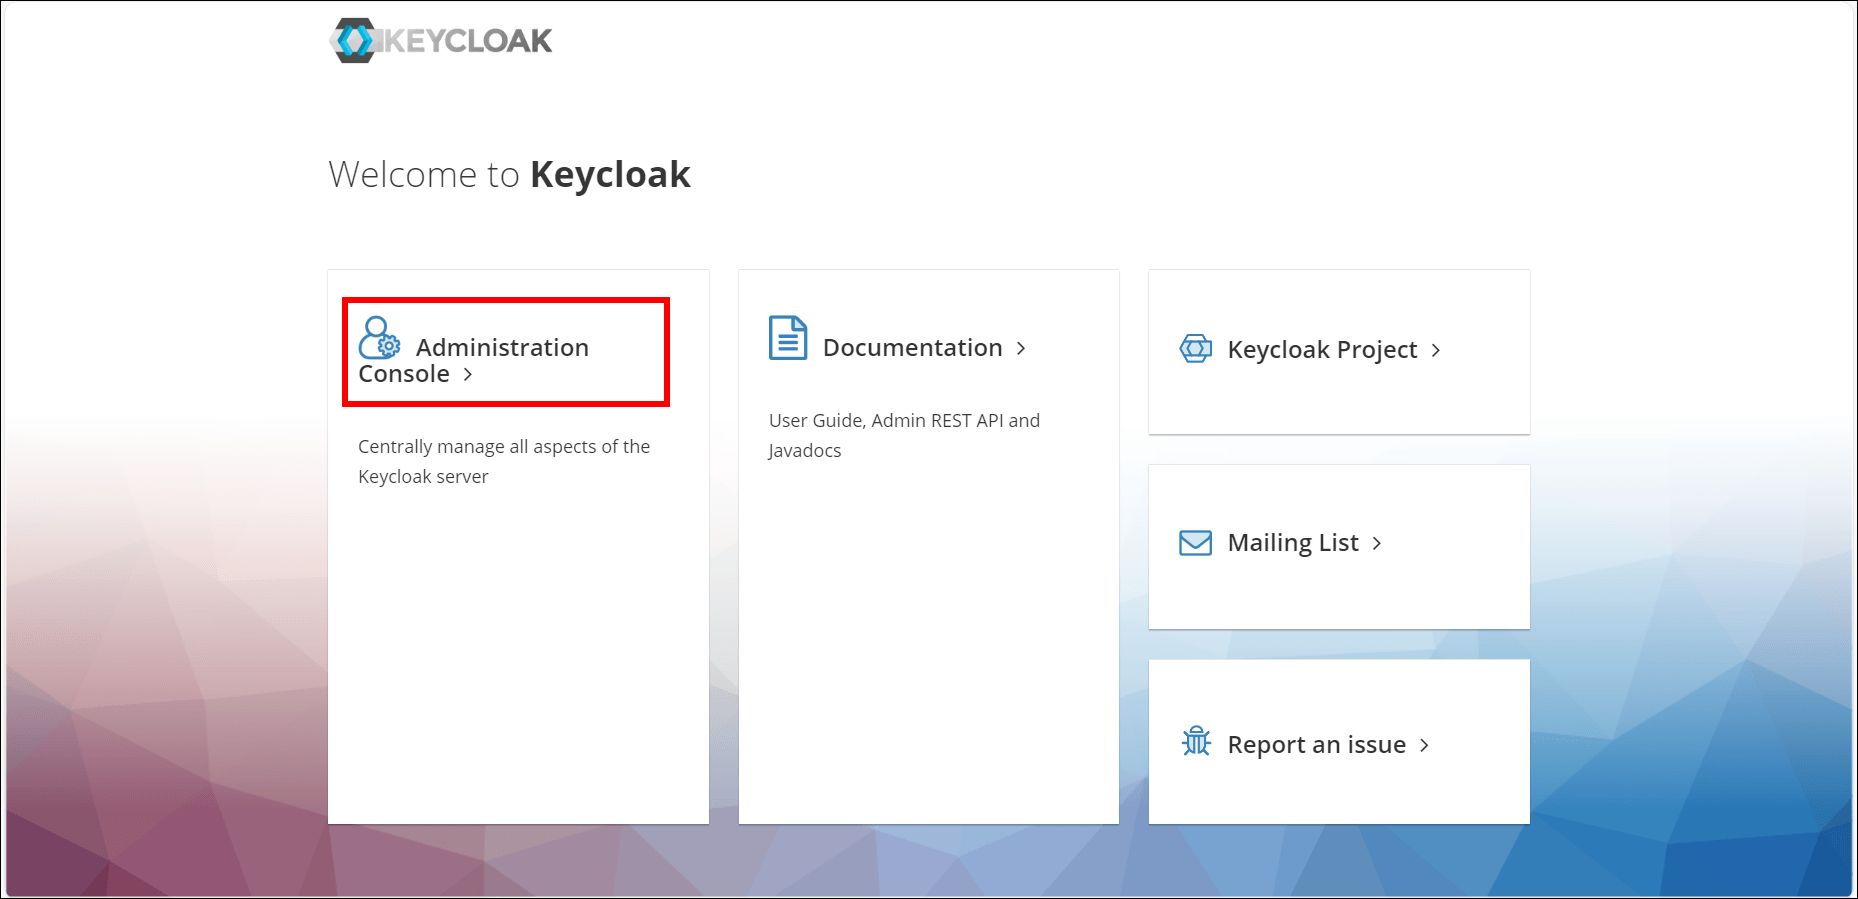
Log in to the Keycloak website with an admin account.
-
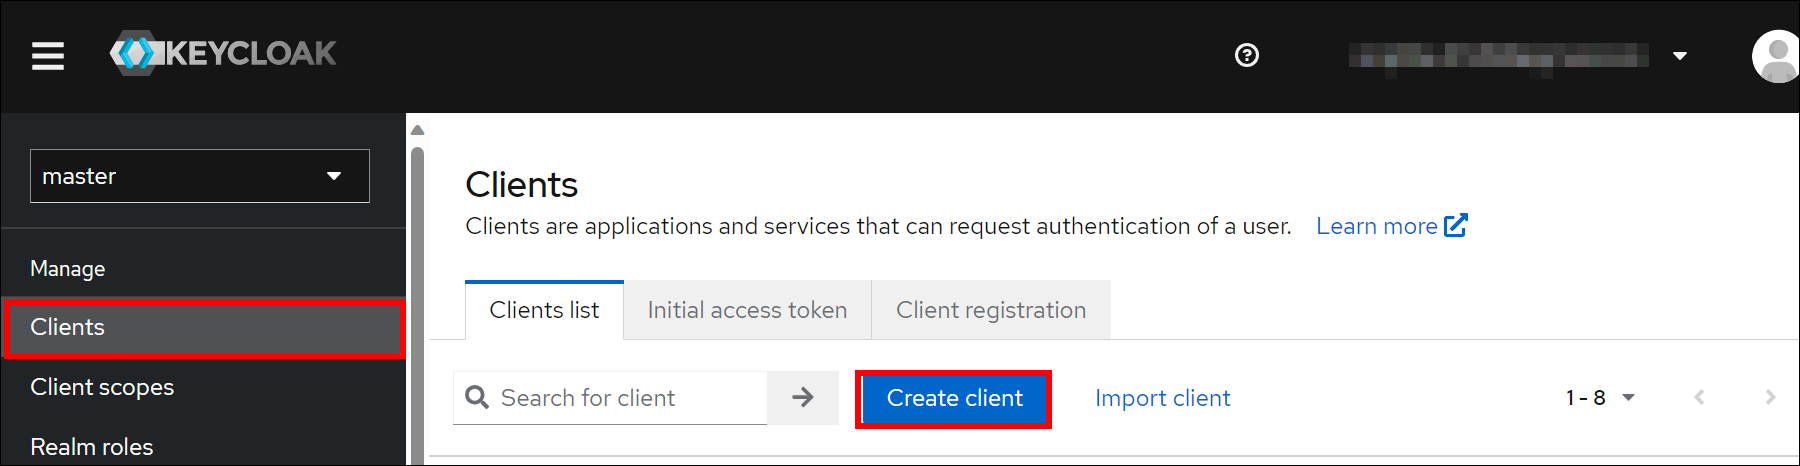
Go to the Security admin console, then to the Clients page, and select the Create client option.
-
On the
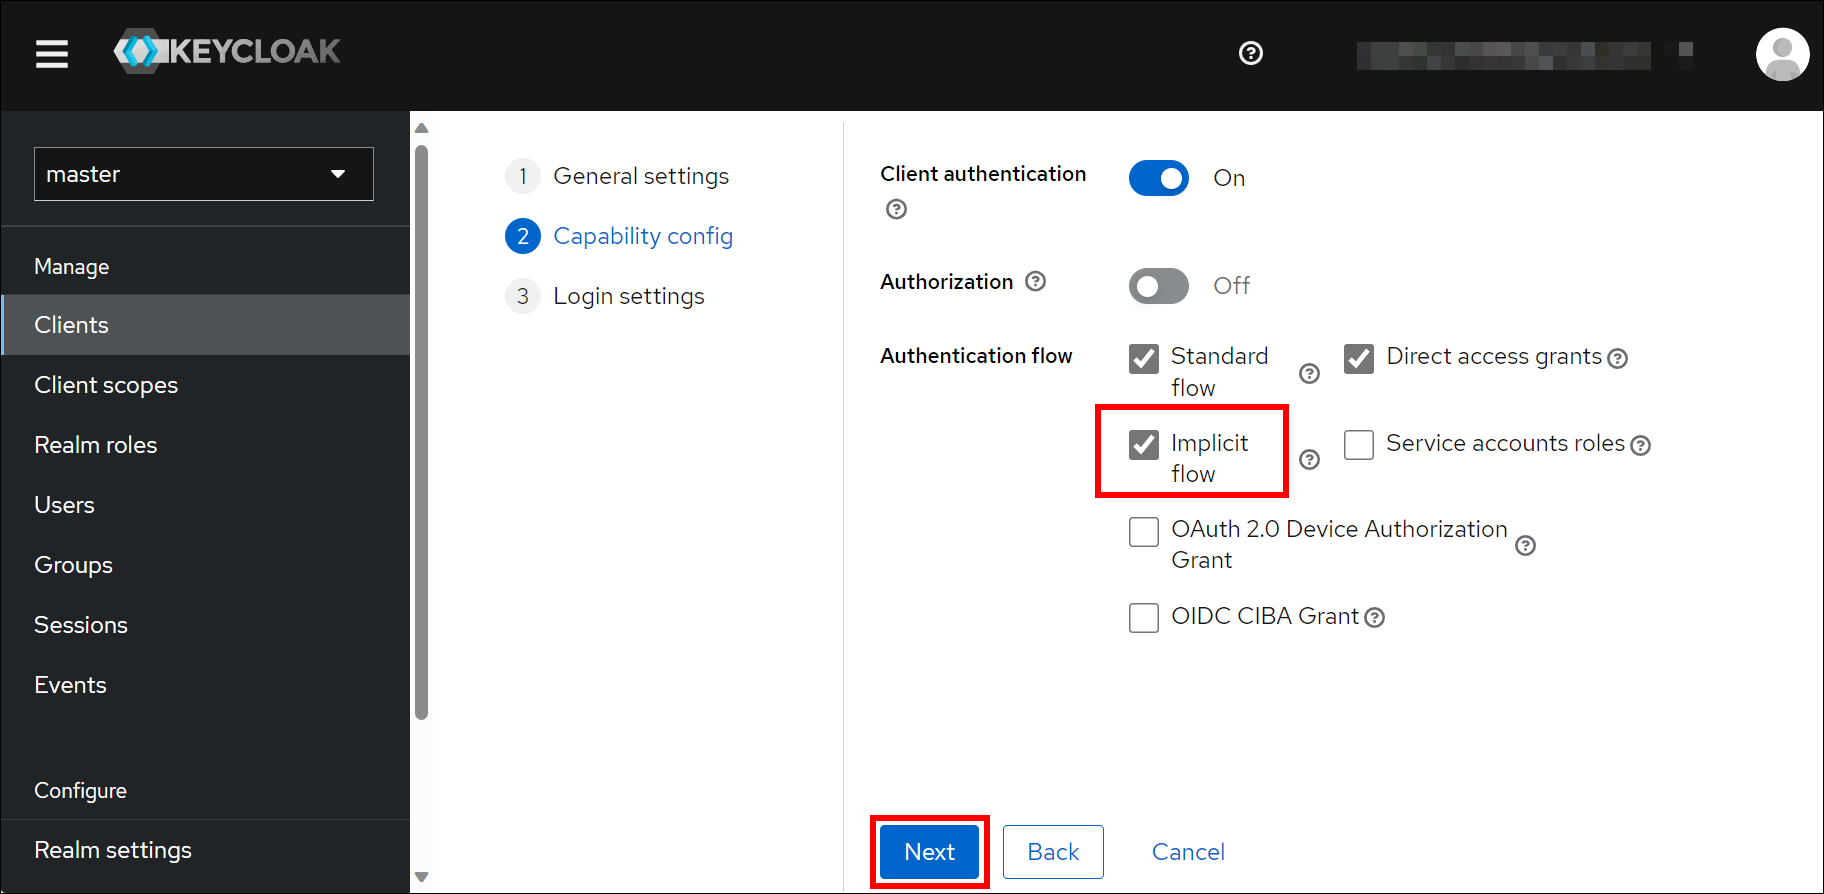
Create Clientpage, enter the client ID and selectopenid-connectas the client protocol. Then, configure the required settings as shown in the following images and save the changes: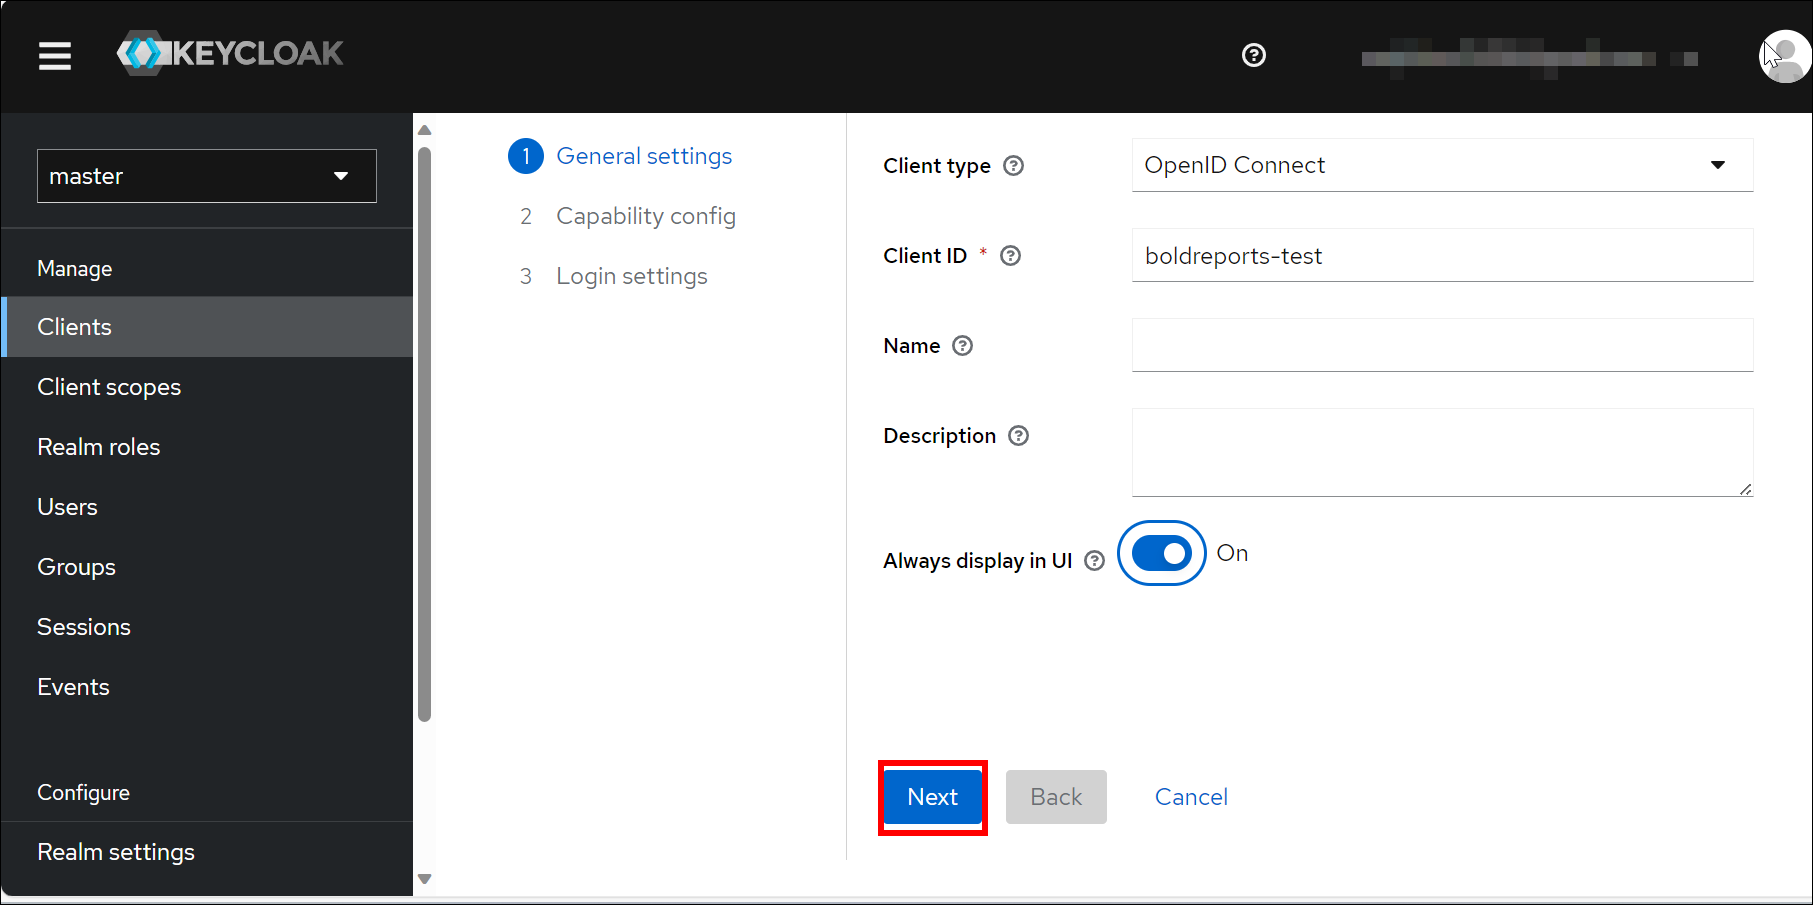
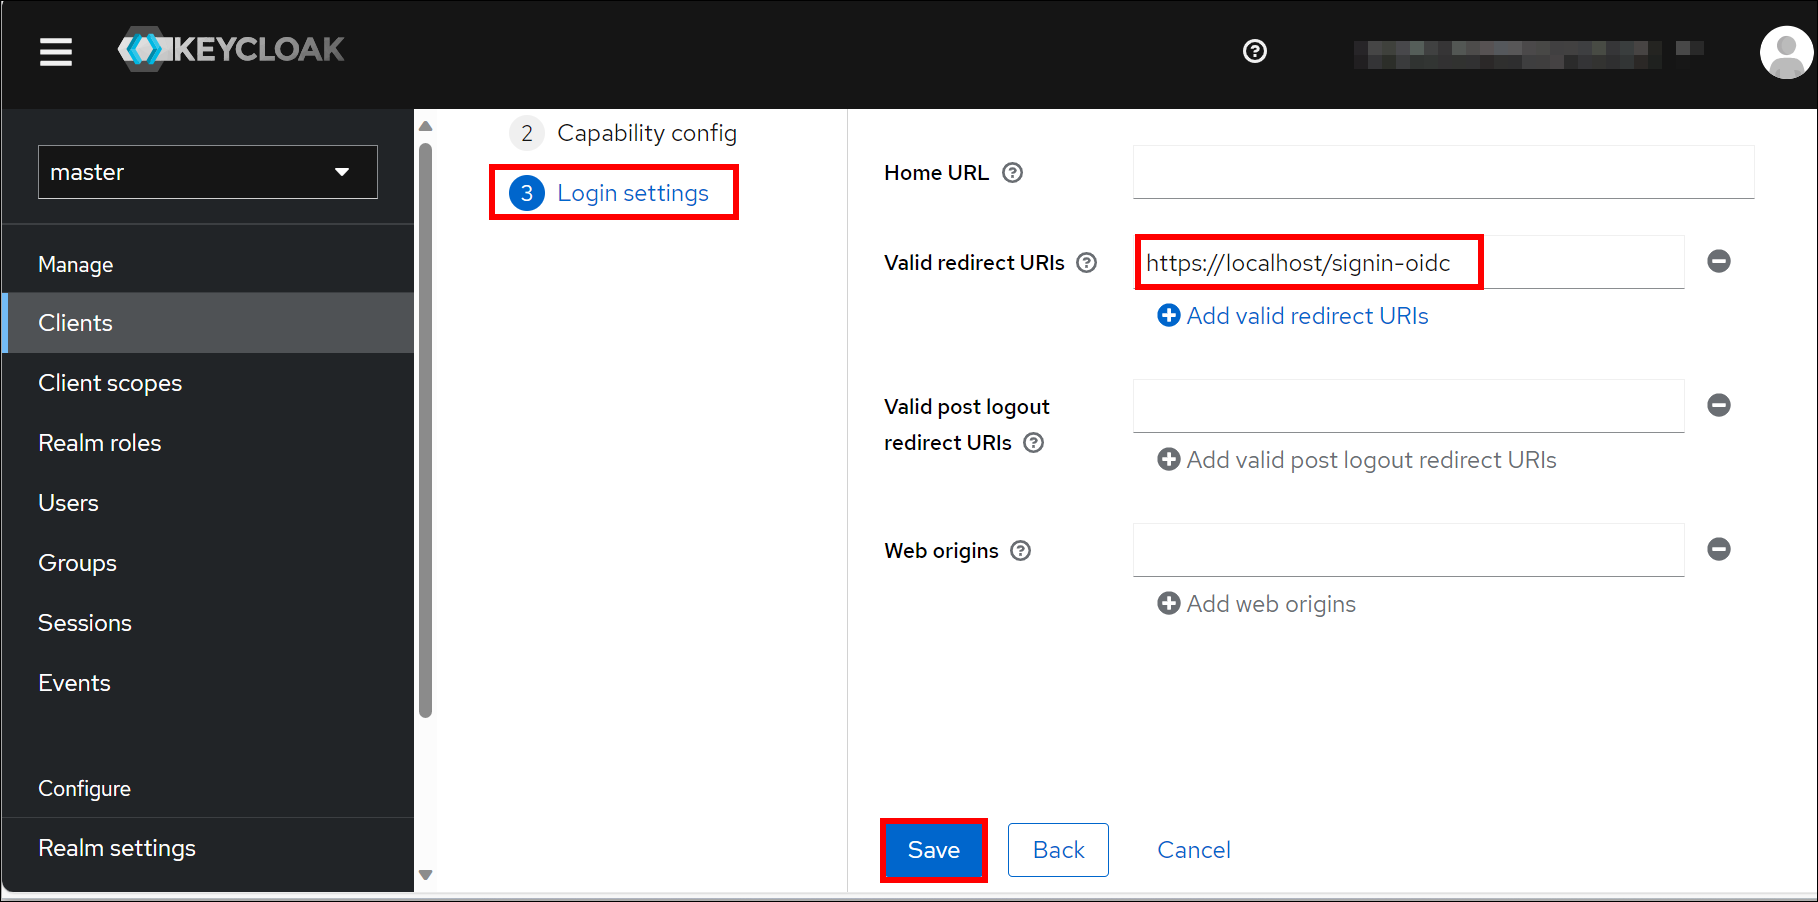
-
After the client is created, you can make updates in the settings section.
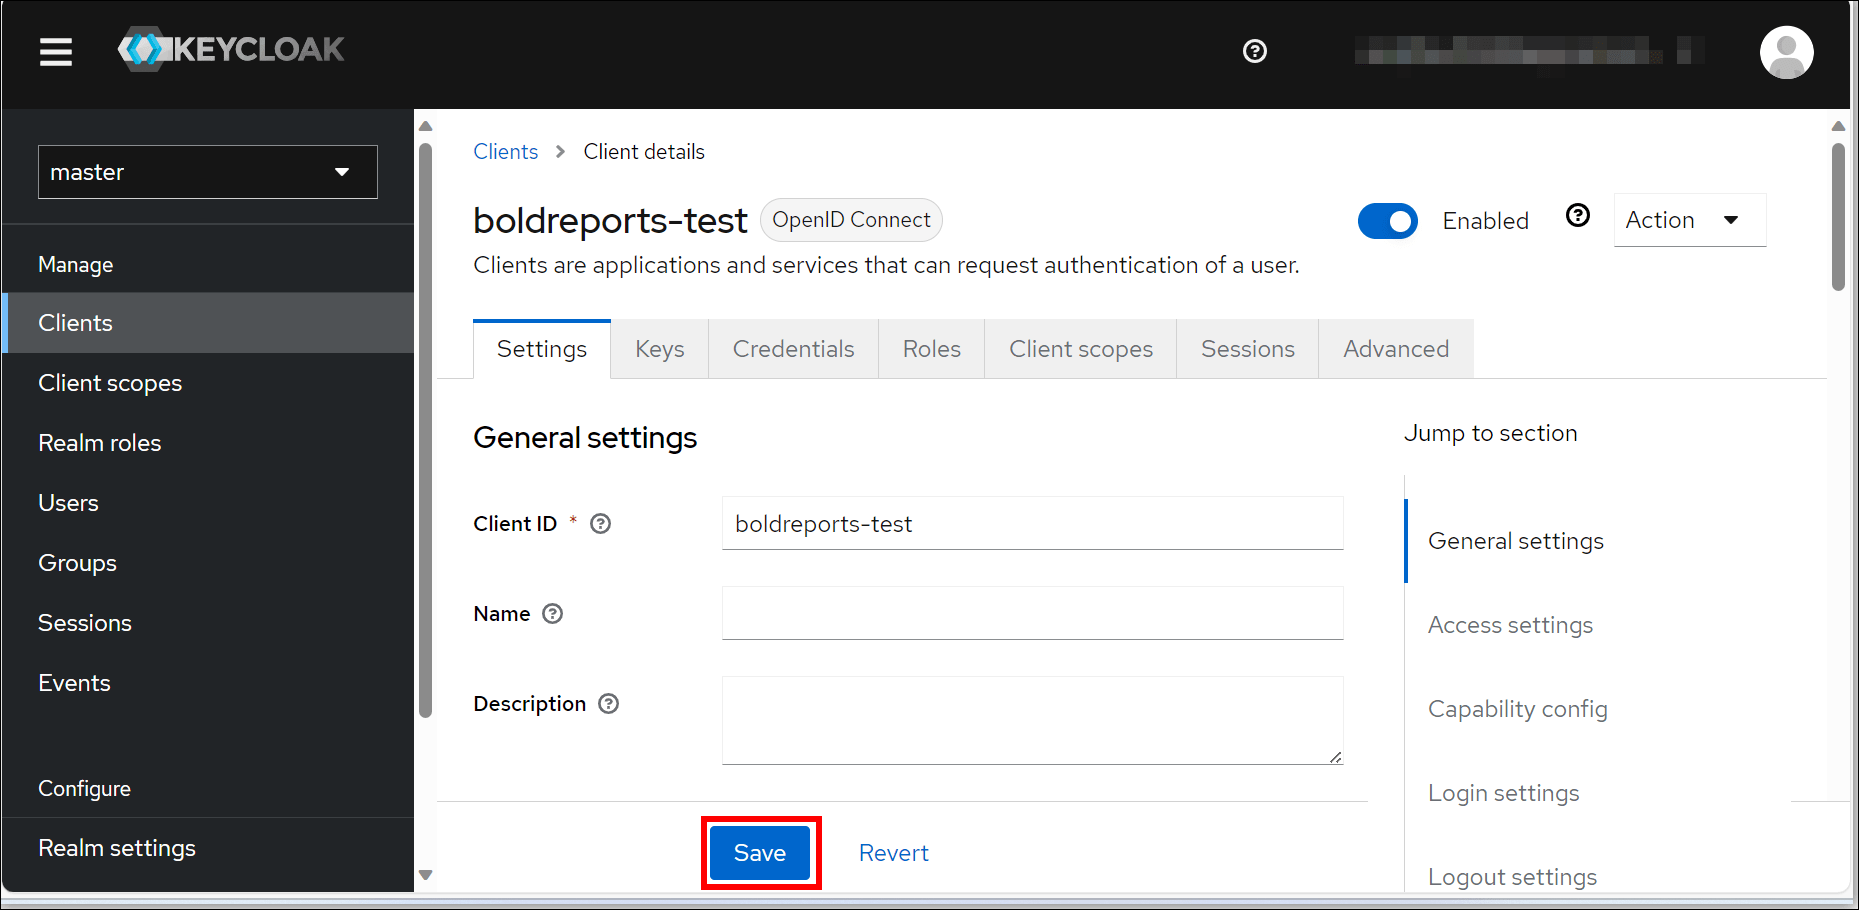
The following table lists the Keycloak client settings to use for Bold Reports®:
| Implicit Flow Enabled | On |
| Valid redirect URIs | URL Format: https://{domain}/signin-oidc Example: https://example.com/signin-oidc Note: The Redirect URI is found under the OpenID Connect settings of your Bold Reports® application, as in the following screenshot. |
Note: When configuring the access type, you can set it to
confidential. After successful registration with Keycloak, save these settings in the Bold Reports® settings page to enable this authentication.
Enable Keycloak authentication support in Bold Reports®
To enable Keycloak authentication in Bold Reports®, configure the OpenID Connect settings as shown in the following screenshots.
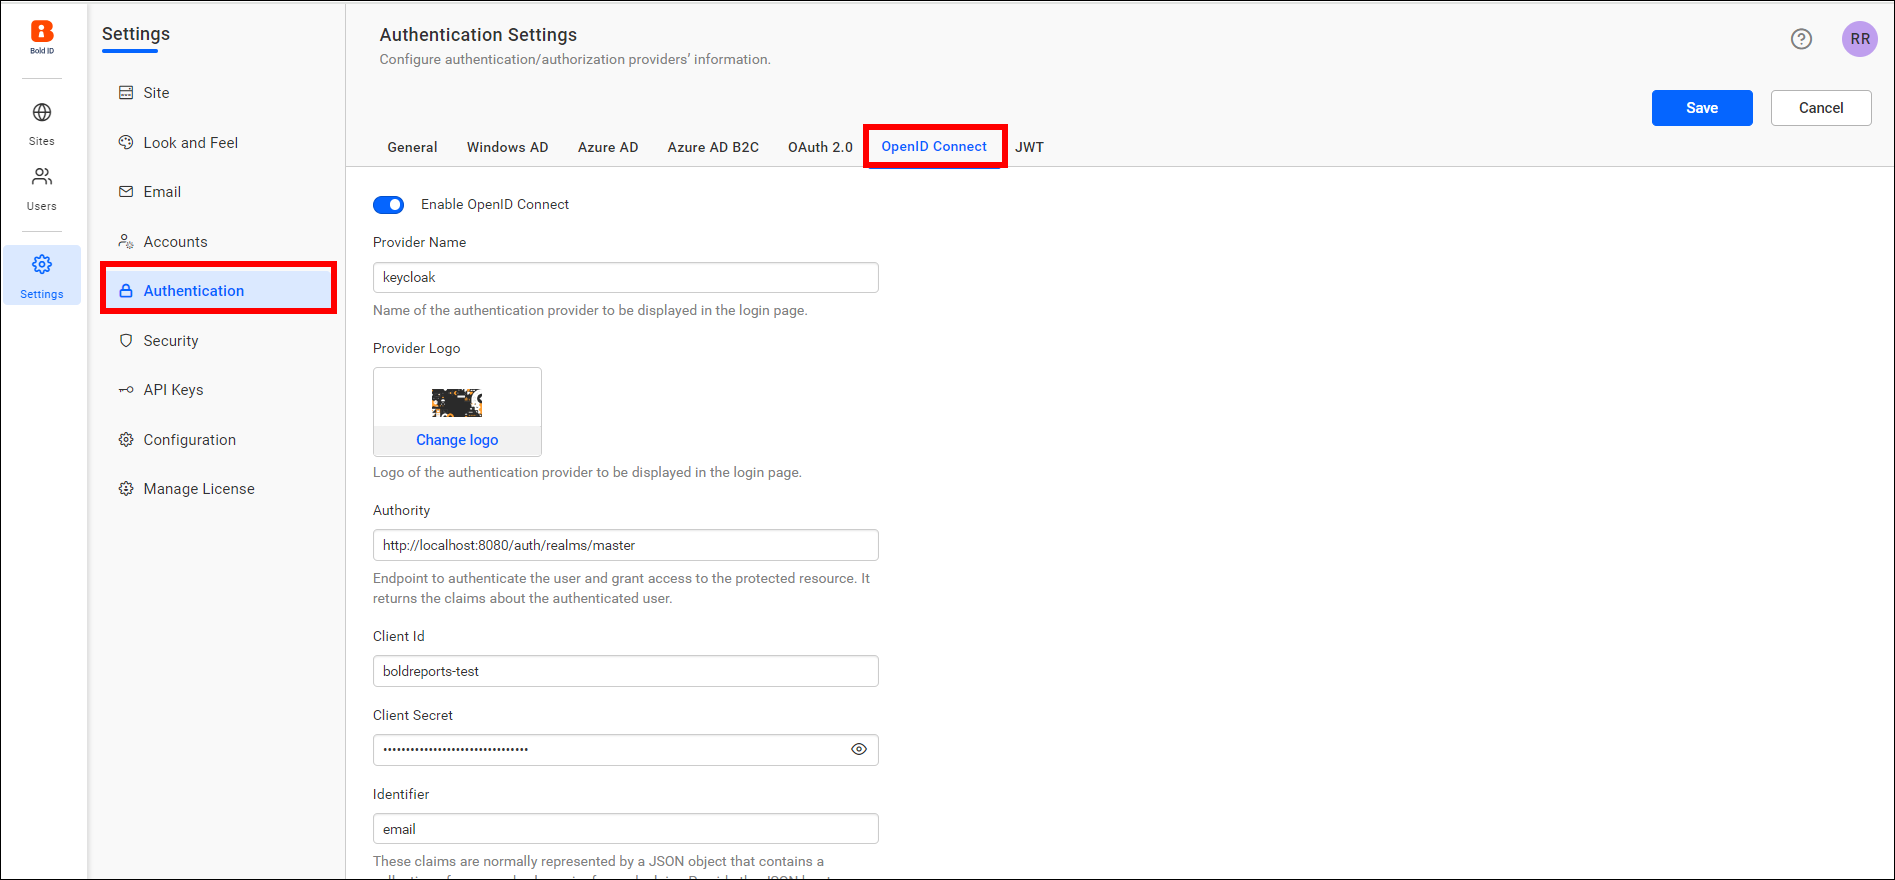
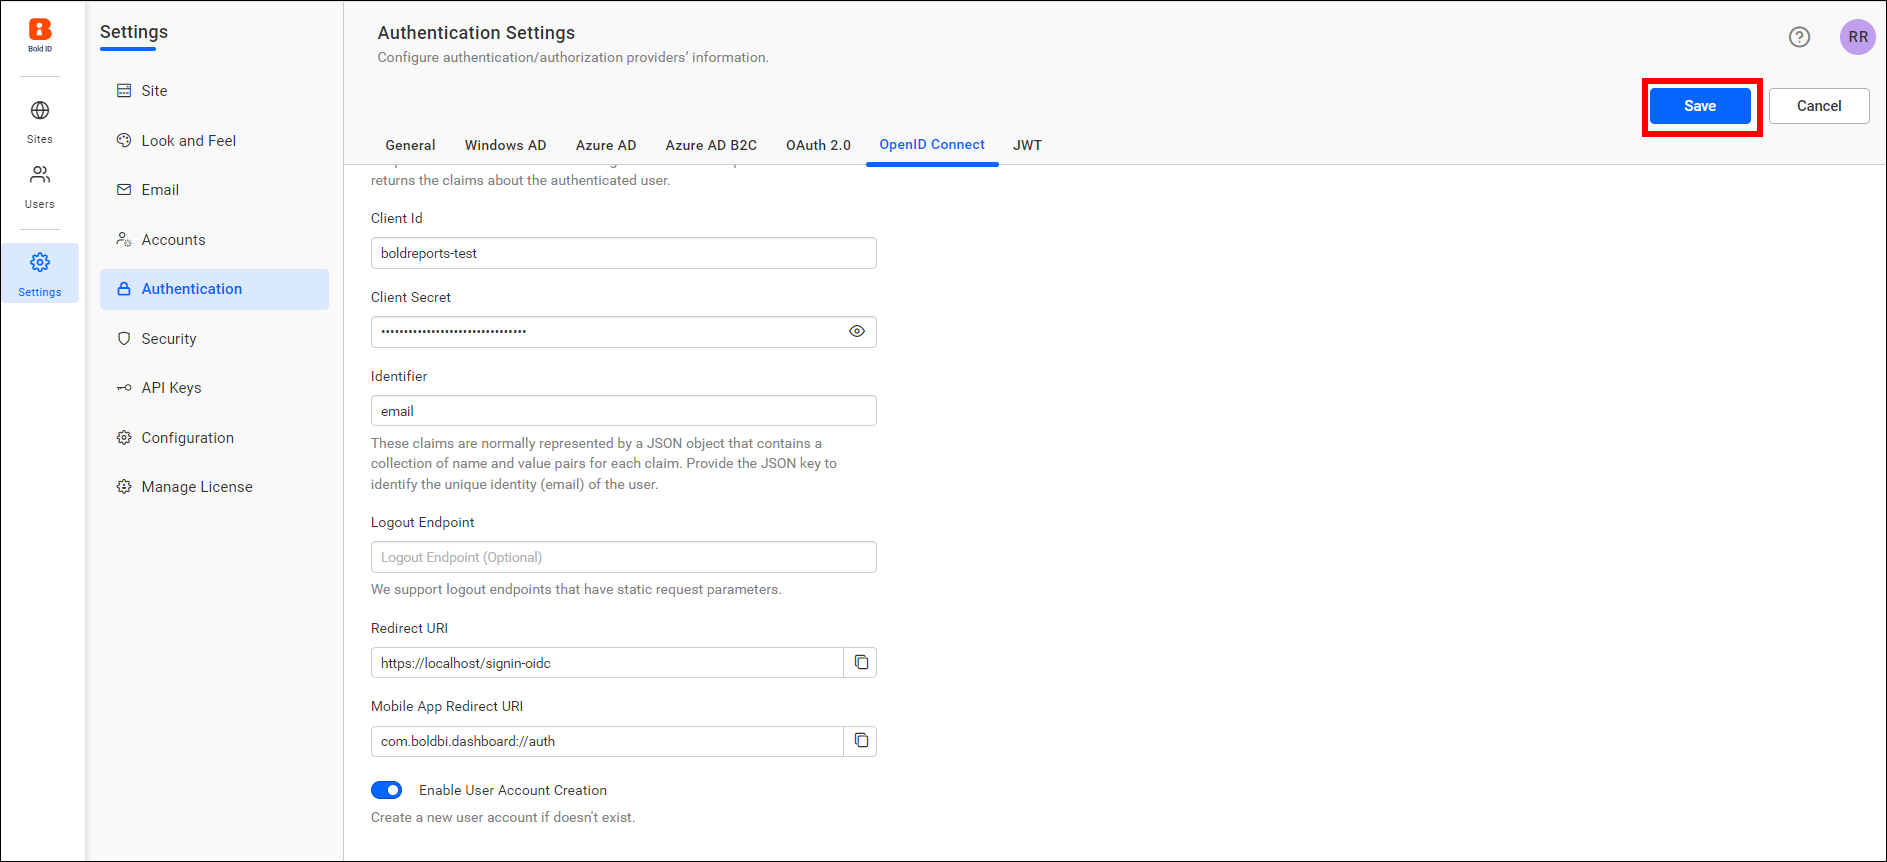
The following table explains the fields you save in Bold Reports® to enable Keycloak for authentication:
| Enable Open ID Connect | Enabled |
| Provider Name | It represents the name of the authentication provider to be displayed on the login page. |
| Provider Logo | It represents the logo of the authentication provider to be displayed on the login page. |
| Authority | It must be the URL of your Keycloak instance. URL format: https://{host}/auth/realms/{realm} Note:The Authority URL only accepts HTTPS, and Keycloak should be configured in HTTPS. |
| Client ID | The client ID is the one you get after registering the Bold Reports® application on the Keycloak website. Note: Client IDs are available on the Clients page of the Keycloak website. |
| Client Secret | The client secret is the one you get after registering the Bold Reports® application on the Keycloak website. Note: Client secrets are available in the Credentials section of the Client Details page. |
| Identifier | The Bold Reports® application requires an email address to log in to the application. So, set the identifier as the email. Note: All accounts in Keycloak should have a valid email address. |
| Logout Endpoint | It is the endpoint on the Keycloak website that signs the user out. |
How do I log in to Bold Reports® with Keycloak?
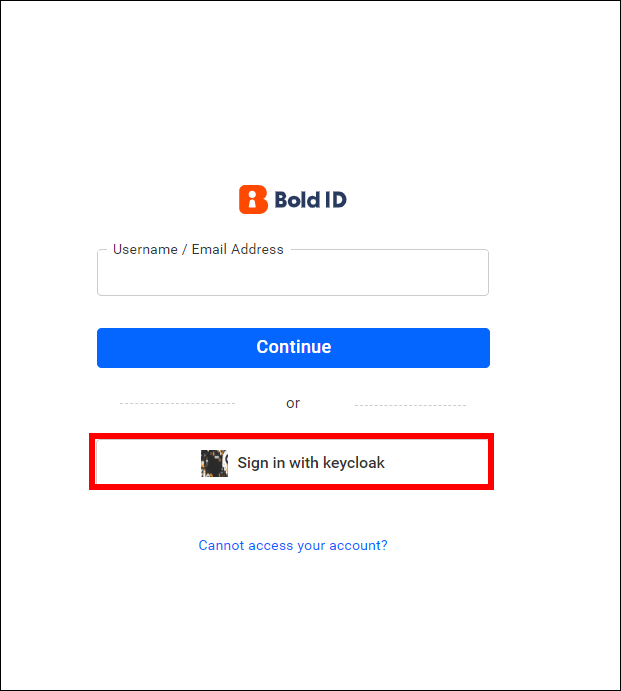
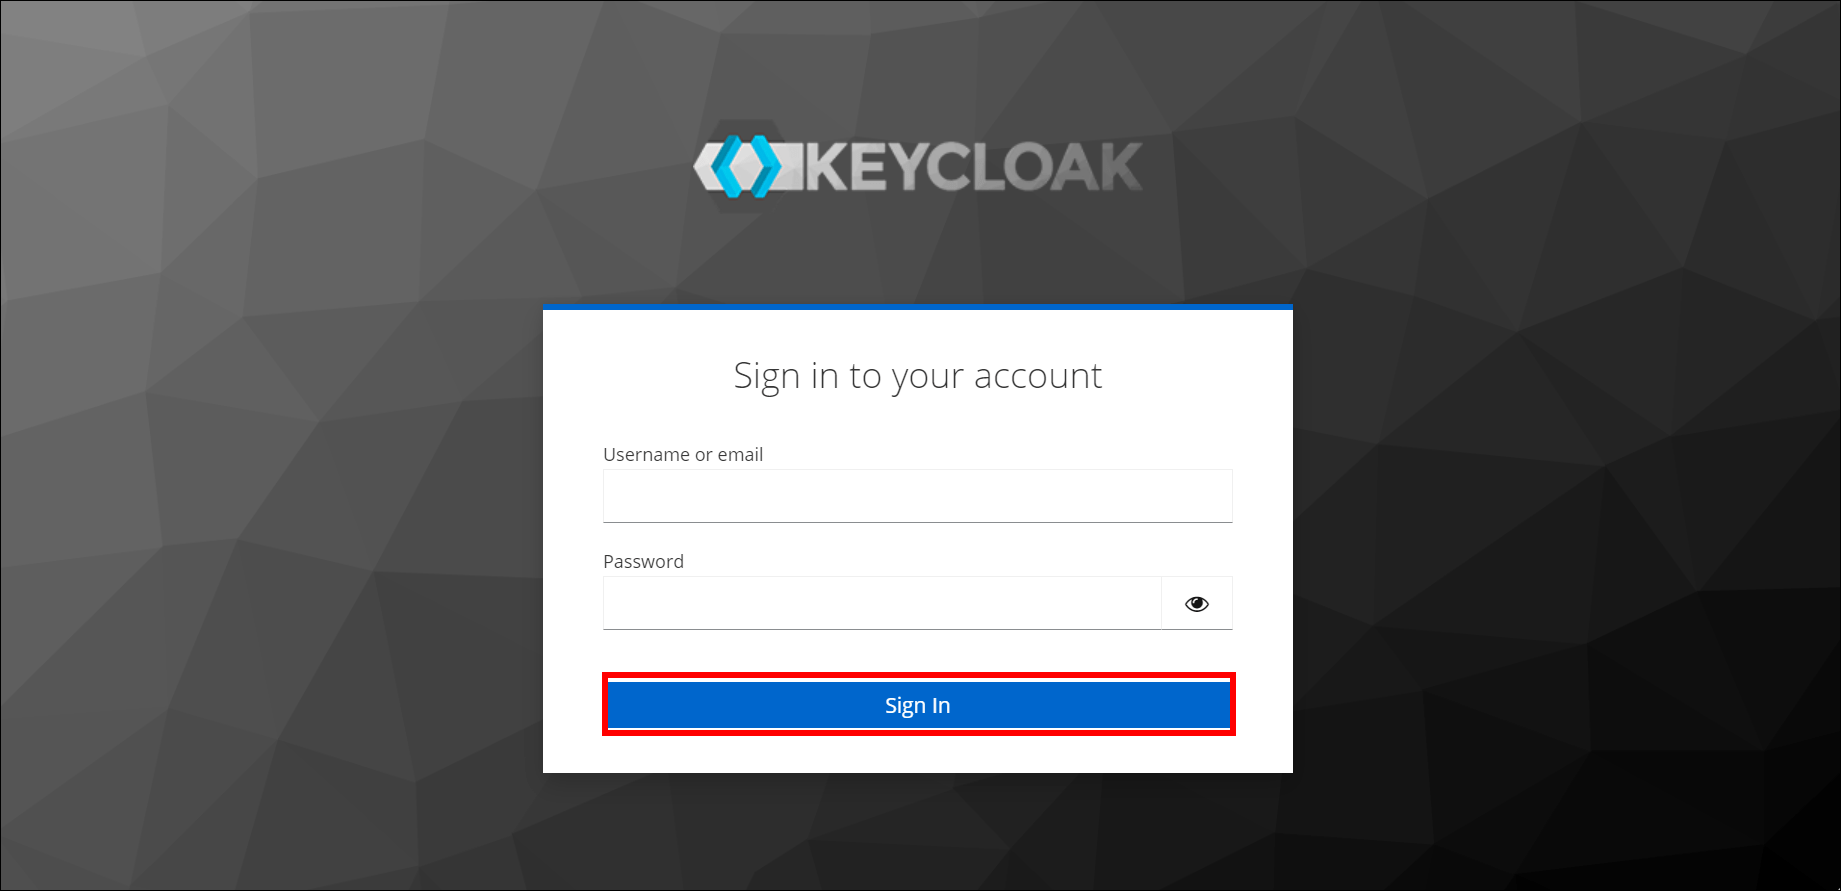
You log in to Bold Reports® with Keycloak from the Bold Reports® login page. Follow these steps:
-
Go to the login page and select the Keycloak option to log in.
-
Fill in the username and password on the Keycloak login screen and sign in.
Frequently asked questions
Does the Keycloak Authority URL support HTTP?
No. The Authority URL in Bold Reports® only accepts HTTPS, and Keycloak should be configured in HTTPS.
Which Identifier do I use for Keycloak in Bold Reports®?
Set the identifier as the email, because Bold Reports® requires an email address to log in. All accounts in Keycloak should have a valid email address.