How do I set a Content Security Policy in Cloud Reporting?
Bold Reports® Cloud supports a Content Security Policy (CSP) that helps protect your site from cross-site scripting (XSS) and data injection attacks. In these attacks, an attacker delivers malicious scripts or unwanted data.
By default, the browser executes resources from any origin without restriction, as it doesn’t know whether a source is trusted. A malicious script can then access cookies, session tokens, or other sensitive information stored by the browser. CSP gives you a standard set of directives for this. The directives tell the browser which content sources are allowed and which are blocked.
How Content Security Policy works
The Content Security Policy (CSP) uses the Content-Security-Policy response header to restrict resource loading from unknown domains. It allows only resources that come from a configured list of trusted domains for each content type. Configure CSP directives to block styles, scripts, fonts, images, connects, and frames from unknown domains. This stops malicious resources from running on your site.
How Content Security Policy affects report rendering
Enabling CSP does not change how reports render in most cases. A report is affected only when it loads resources from an unknown domain that your CSP settings do not allow. If you intend to load resources for your reports from an external URL, you must include that URL in the appropriate sources section of the CSP settings.
Where to configure Content Security Policy
You configure the Content Security Policy on the Content Security Policy tab of the Security settings page.
By default, the Content Security Policy is disabled, allowing sources from all domains without restriction. As a result, the Content-Security-Policy response header will not be added to the request.

How to enable Content Security Policy
To enable Content Security Policy, select the Enable Content-Security-Policy check box on the Content Security Policy tab of the Security settings.
If you enable the Content-Security-Policy option, the Content-Security-Policy response header will be added to the request, including the default allowed domain values for each source.

Which CSP directives can you configure?
You can set allowed URLs for six CSP directives. Each field adds its URLs to the matching directive, together with 'self'.
| Settings field | Directive | What it allows |
|---|---|---|
| Style Source | style-src |
Style sheets |
| Script Source | script-src |
JavaScript sources |
| Font Source | font-src |
Fonts |
| Image Source | img-src |
Images |
| Connect Source | connect-src |
Fetch and XHR requests |
| Frame Source | frame-src |
Nested documents in <frame> and <iframe> elements |
How to configure the style source policy
The style-src directive allows only the URLs of style sheets that are added in the Style Source field and restricts style sheets from other URLs.
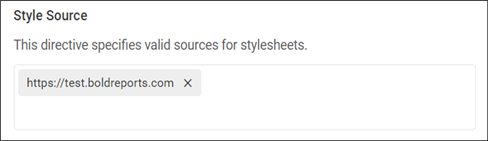
The permitted URLs will be added to the Content-Security-Policy for the style source.
Content-Security-Policy: style-src 'self' https://test.boldreports.com
How to configure the script source policy
The script-src directive allows only JavaScript sources from URLs added in the Script Source field and restricts script sources from other URLs.
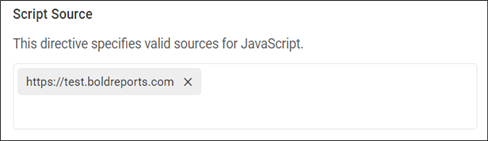
The permitted URLs will be added to the Content-Security-Policy for the script source as follows:
Content-Security-Policy: script-src 'self' https://test.boldreports.com
How to configure the font source policy
The font-src directive allows font sources only from URLs added in the Font Source field and restricts font sources from other URLs.
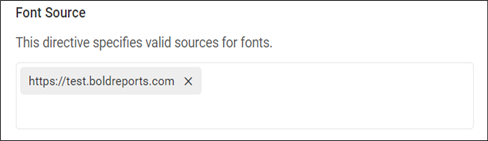
The permitted URLs will be added to the Content-Security-Policy for the font source as follows:
Content-Security-Policy: font-src 'self' https://test.boldreports.com
How to configure the image source policy
The img-src directive allows images only from URLs added in the Image Source field and restricts image sources from other URLs.
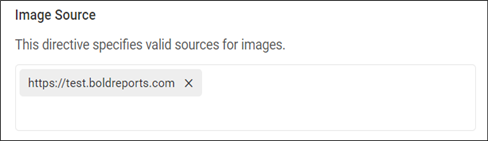
The permitted URLs will be added to the Content-Security-Policy for the image source as follows:
Content-Security-Policy: img-src 'self' https://test.boldreports.com
How to configure the connect source policy
The connect-src directive allows Fetch/XHR requests only from URLs added in the Connect Source field and restricts Fetch/XHR requests from other URLs.
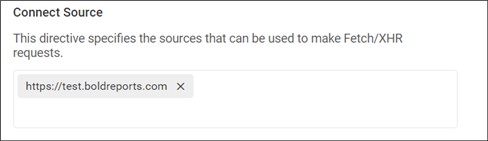
The permitted URLs will be added to the Content-Security-Policy for the connect source as follows:
Content-Security-Policy: connect-src 'self' https://test.boldreports.com
How to configure the frame source policy
The frame-src directive allows sources for nested documents to use elements such as <frame> and <iframe> only from URLs added in the Frame Source field, and restricts sources from other URLs.
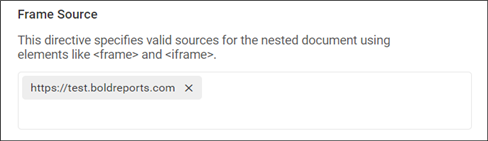
The permitted URLs will be added to the Content-Security-Policy for the frame source.
Content-Security-Policy: frame-src 'self' https://test.boldreports.com
Frequently asked questions
Is Content Security Policy enabled by default in Cloud Reporting?
No. Content Security Policy is disabled by default, so resources load from all domains and the Content-Security-Policy header is not added.
How do I allow a report to load resources from an external URL?
Add the external URL to the matching source field in the CSP settings, such as Image Source for images or Font Source for fonts. Otherwise, the browser blocks that resource.
Which directive controls content loaded in an iframe?
The frame-src directive controls it. Add trusted URLs to the Frame Source field to allow nested documents in <frame> and <iframe> elements from those URLs.